
How Rosanna Bellini Is Helping Make Digital Platforms Safer from Interpersonal Threats
Technology is often designed around an implicit assumption: the person using it has good intentions. But what happens when the person controlling a family phone plan, a shared financial account, or a connected device is motivated to use those privileges against someone they know, or are in an intimate relationship with?
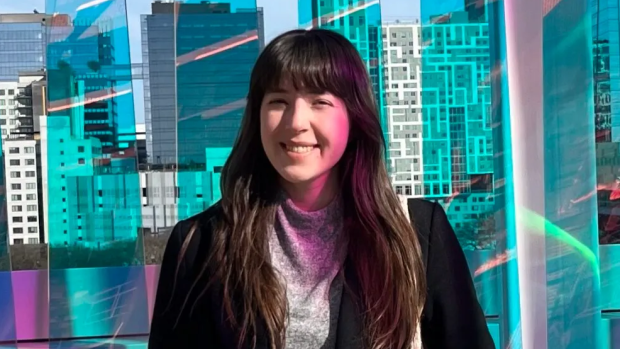
That question sits at the center of Rosanna Bellini’s research. An Assistant Professor of Computer Science and Engineering at NYU Tandon, Bellini works in digital safety, an emerging field at the intersection of human-computer interaction, and security and privacy. Her research examines how technology can enable intimate partner violence, financial abuse, surveillance, and other forms of interpersonal harm, as well as how designers, engineers, and policymakers can make systems safer. Her research recently landed her on the highly competitive MIT Technology Review’s “35 Innovators Under 35” list. This year MIT Technology Review said it received 550 nominations from around the world, both from its staff and the public. Editors narrowed these down to 110 semi-finalists who were then evaluated by 44 judges before picking winners across four categories: AI, biotechnology, climate and energy, and computing and robotics.
We spoke with Rosanna about why conventional cybersecurity models often miss interpersonal abuse, how generative AI is lowering the barrier to technology-enabled harm, and how engineers need to think more carefully about who might misuse the systems they build.
How would you describe the focus of your research?
My research focuses on ensuring systems are safer for at-risk users; groups who use digital systems who are at an elevated level of risk compared to a general user, and can’t easily recover from cyberattacks when they happen. I specialize in situations where privacy and security assumptions break down when we make incorrect assumptions about adversaries, such as involving interpersonal abuse or financial control.
I then derive threat intelligence that can help us understand and discourage those behaviors, better support survivors who are being targeted by building services that help them, and make technology harder to abuse in the first place. It’s pretty challenging, but I think it’s absolutely worth stepping up to the challenge as designing for at-risk users also benefits general users too.
How has your understanding of the relationship between technology and interpersonal harm changed over the course of your career?
I’ve always been interested in interpersonal abuse because it was a scenario that was frequently left off the table in technology development, despite it being experienced by 1 in 3 women and 1 in 6 men over their lifetime. Over the course of my career, that has made my resolve stronger to make space for these extremely common situations. I’ve witnessed everyday digital technologies and services being used for harassment, stalking, monitoring, and financial control, and I wanted to dedicate my time to changing this.
If we aren’t representing interpersonal harm in the way we design technology, there is a high chance that we are making things worse. Intimate partner violence is often misunderstood as being primarily about physical violence, but it is better understood as a pattern of coercive behavior in which one partner controls another. From that perspective, technology that doesn’t anticipate this threat can become another lever of control. My research tries to empirically study many of these underlying interpersonal dynamics that aren’t normally represented in the design of everyday technologies and ask whether privacy, security, or technology design is exacerbating them.
Then we can work directly with technology companies and policymakers to target where the vulnerabilities are, either patch or write legislation that resolves this to actually make a difference to millions of users.
What do conventional approaches to cybersecurity tend to miss when the person posing the threat is someone the victim knows personally?
Psychologically, we don’t like to think about a person we know personally causing harm. It might make us feel more psychologically safe to think of strangers targeting our devices, but there’s a solid possibility that it might be someone close to us, like a partner or acquaintance.
When we talk about interpersonal abuse, we tend to focus on survivors. But those survivors become survivors because of someone causing abuse, and this has a knock-on effect that we describe these phenomena without the responsible agents. We might talk about the number of survivors of intimate partner violence, but we talk much less about the people committing that abuse and what drives them to behave that way.
You can see that reflected in digital safety tooling; the responsibility is for the targets of such attacks to keep themselves safe. If we only focus on survivors, we place an enormous amount of responsibility on people who are already being targeted by severe harm. This is not just unfair, but it’s also unlikely to be effective over time as the adversary will just continue without being challenged.
The other issue is that traditional threat models don’t always work very well when the adversary knows the target personally. These individuals might not be purely financially motivated. They may have complicated social goals. It could be financial control, intimidation, public humiliation, or surveillance.
I’m excited to see that cybersecurity has begun moving away from the assumption that every adversary is simply financially motivated and that shift can help us think much more broadly about what technologies make people safer.
What would it mean to design technology with coercive control and unequal power dynamics in mind?
We need to start by challenging some of our core assumptions about technology.
It isn’t always one person per device. The “super user” on a family account isn’t necessarily a benign user. When we create family accounts or joint accounts, we naturally presume that the people with additional privileges have good intentions. We often don’t model what happens if one of those users does not have good intentions toward the rest of the group.
Could someone use their privileges on a shared phone plan to stalk or surveil members of their family? If you allow someone to receive spending alerts about another person, are they genuinely helping that person, or are they financially surveilling them?
These features were usually created to provide some positive benefit for an unmet user need. But technology can be dual use. Someone can take advantage of a feature for a purpose it was never intended to serve.
There are strategies that I’m personally developing so that we can build safer technologies for all such as making abusability testing frameworks to model how interpersonal abuse might play out in the systems we use every day. There will always be trade-offs, but companies should still ask what social responsibility they have to their users to ensure that putting a product or system into the world does not create additional harm.
How is generative AI changing the landscape of technology-enabled abuse?
Generative AI has unfortunately lowered the barrier to abuse for a significant number of people looking to cause harm. This technology has made automating certain kinds of abuse much more accessible.
Previously, someone who wanted to stalk or monitor their partner might have had to scour the internet looking for information about how to do it. Now they may be able to use an AI system to compile information for them, particularly if they phrase the request under the guise of protecting or helping someone. Alternatively, they could initialize an agent to harass someone on their behalf.
Generative AI lowers the technical barrier to entry for conducting these attacks, and creates entire communities of enthusiasts online who can share tips and tricks for achieving this successfully. As the barriers continue to lower, as designers and developers, we also need to understand abusive adversaries more; what motivates them, what tactics they might use, and how to disrupt the communities that form around them.
What role should technology companies and governments play in addressing these problems?
We’ve made a lot of progress in pushing for progressive protectors for all users under improving consumer rights protection laws. While not everyone can be framed as a consumer, seeing how
I think there is a lot of potential in encouraging cross-sector collaboration rather than competition, particularly for harms that manifest across platforms. If someone produces nonconsensual intimate imagery, for example, it probably isn’t going to remain on one platform. It may spread across many of them. This kind of cross-company collaboration can be difficult because these companies are competitors. But there is also a business case for it. No single company has to provide all of the resources to fight these problems by itself. Companies can lean on one another and on outside experts.
One model is StopNCII, where technology companies collaborate around systems that can identify known intimate imagery so that participating platforms can recognize it and take action.
You also see financial abuse as an important emerging area for digital safety. Why?
A huge amount of our financial lives has gone digital, so many of the technology-abuse vectors we see elsewhere are beginning to appear in financial systems as well.
Financial abuse is often quite hidden. But if someone controls your money, they control you.
If we can make financial coercion, financial control, or identity theft harder to achieve, then there is an increased chance that even a highly motivated adversary will work out that it simply isn’t effective. Doing so can create technologies that give people much more freedom and independence. There is a lot of potential for digital safety research to contribute to that.
Given the scale of these problems, what makes you optimistic?
Technology-enabled abuse is certainly a growing challenge. Yet something I’m really excited about is seeing a new generation of people interested in digital safety and companies responding to emerging research on specific ways they can improve their technologies.
Many students and young people either have personal experience with these issues or know somebody who does. They come to me with deep expertise in a particular area and want to apply it somehow, whether that is cybersecurity and privacy, research, or technical design.That gives me hope for the next generation of engineers, designers, and developers.
It can sometimes feel like we’re fighting a losing battle because technology changes so quickly and there are always new ways for it to be abused. But I see a lot of people who genuinely want to mitigate these harms.
I saw that when I taught Trust and Safety. The number of students who signed up and really engaged with these questions was encouraging. It suggests that more people entering technical fields understand that safety isn’t something you add after a system has been built. It is something you need to think about from the beginning.